Essential Cybersecurity and IT Security Solutions Built for Law Firms
Law firms sit on some of the most sensitive data, including client records, case files, financial details, and privileged communications. That makes them an attractive target for cybercriminals, and it’s exactly why Cybersecurity Services For Law Firms have become a non-negotiable part of running a modern practice, regardless of firm size. Attorneys are entrusted with information clients expect to stay confidential, and any lapse in protection can have consequences that go well beyond a simple IT inconvenience.
A single breach can mean more than financial loss. It can compromise client confidentiality, damage a firm’s reputation, and even raise questions about compliance with bar association and data protection rules. This guide breaks down what firms need to look for and why the right security partner matters.
Why Law Firms Are a Prime Target for Cyberattacks
Law firms often hold more sensitive data per client than many other industries, yet many still operate with outdated systems or limited in-house IT support. That combination makes them appealing targets for attackers looking for high-value information with comparatively low resistance.
Common risks law firms face include:
- Phishing attempts targeting attorneys and staff with access to sensitive files.
- Ransomware attacks that lock down case files and demand payment for their release.
- Unauthorized access to confidential client communications.
- Data breaches that trigger regulatory and bar association scrutiny.
- Business email compromise targeting trust accounts and wire transfers.
Building Strong Law Firm IT Security
A solid security foundation starts with more than just antivirus software. Effective Law Firm IT Security typically includes network protection, endpoint monitoring, regular vulnerability assessments, and strict access controls that limit who can view specific case files.
It also means having a plan in place before something goes wrong, not scrambling to figure one out after a breach has already occurred.
Network and Endpoint Protection
Every device connected to a firm’s systems, from office desktops to attorneys’ personal laptops, needs to be monitored and protected against malware, unauthorized access, and suspicious activity.
Data Encryption
Client files, emails, and case documents should be encrypted both at rest and in transit, so that even intercepted data remains unreadable to unauthorized parties.
Access Controls and Permissions
Not every staff member needs access to every case file. Role-based permissions help ensure sensitive information is only visible to those who genuinely need it.
24/7 Monitoring and Incident Response
Threats don’t wait for business hours. Continuous monitoring helps catch suspicious activity early, while a clear incident response plan minimizes damage if something does slip through.
Secure Collaboration for Modern Legal Teams
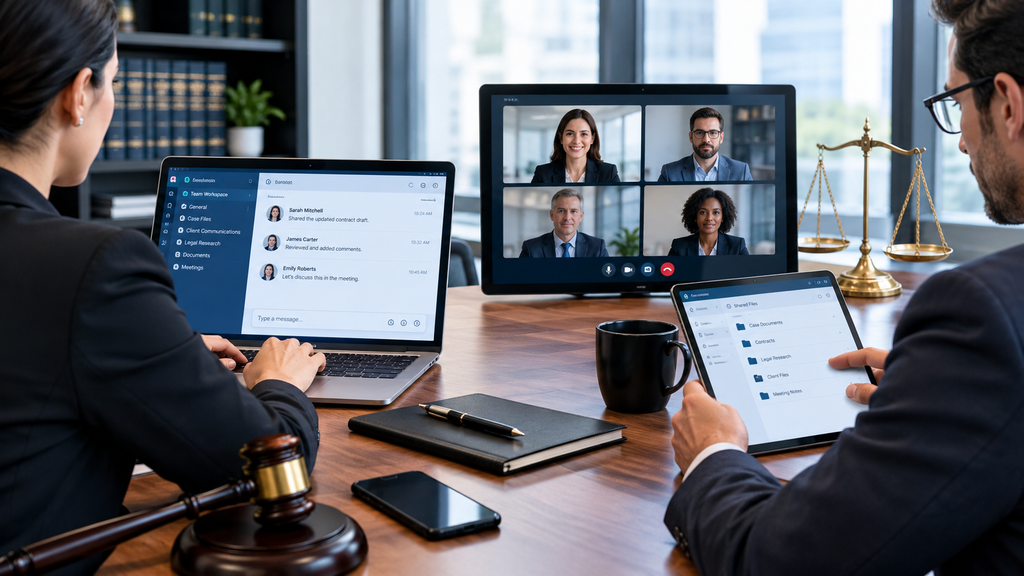
Legal work increasingly involves remote attorneys, outside counsel, and clients who need to share sensitive documents quickly and securely. This is where Law Firm Secure Collaboration Solutions come into play, allowing teams to work together across locations without exposing confidential files to unnecessary risk.
The right collaboration tools should include encrypted file sharing, secure client portals, and detailed audit trails showing who accessed a document and when, giving firms both convenience and accountability.
Benefits of a Strong Cybersecurity Program for Law Firms
Investing in proper security isn’t just about avoiding disaster. It also delivers real, everyday advantages:
- Stronger client trust and confidence in how their information is handled.
- Reduced risk of costly breaches, downtime, and regulatory penalties.
- Improved compliance with data protection and bar association requirements.
- Faster, more organized recovery if an incident does occur.
- A more efficient, secure way for teams to collaborate on active cases.
How to Choose the Right Security Partner
Not every IT provider understands the specific compliance and confidentiality demands of legal work. When evaluating a partner, look for:
- Experience working specifically with law firms or other regulated industries.
- A track record of handling sensitive, privileged data securely.
- Clear incident response procedures and defined response times.
- Scalable solutions that can grow with the firm’s caseload and staff.
- Transparent pricing and a straightforward service agreement.
Final Thoughts
Cybersecurity is no longer optional for law firms it’s a core part of protecting clients, maintaining trust, and staying compliant in an increasingly regulated industry. From network protection to secure collaboration tools, the right combination of safeguards keeps sensitive legal work protected at every stage, whether a firm operates from a single office or across multiple locations with remote attorneys and outside counsel involved in daily casework.
Axelris Technologies International works with legal practices to build security programs suited to the unique demands of handling privileged, confidential information. From initial assessments to ongoing monitoring and support, the goal is to help firms focus on their casework with full confidence in the systems protecting it.
FAQs
1. Why do law firms need specialized cybersecurity services?
Law firms handle highly sensitive, privileged data that makes them attractive targets. Cybersecurity Services For Law Firms address risks generic IT support often overlooks, like confidentiality and compliance obligations.
2. What does Law Firm IT Security typically include?
It usually covers network protection, endpoint monitoring, encryption, access controls, and regular vulnerability assessments tailored to a firm’s caseload and staff structure.
3. How does secure collaboration help legal teams?
It allows attorneys, staff, and clients to share documents remotely without compromising confidentiality, using encrypted channels and detailed access logs for accountability.
4. Are small law firms at risk, or just large ones?
Firms of all sizes are targeted. Smaller firms are sometimes seen as easier targets due to limited in-house security resources.
5. How often should a law firm review its cybersecurity measures?
At least once a year, or whenever there’s a significant change such as new staff, new systems, or updated compliance requirements.
Your Clients’ Trust Deserves Airtight Security
Axelris Technologies International helps law firms protect privileged data, stay compliant, and collaborate securely without slowing down casework. Get in touch today to build a security plan built for your practice.